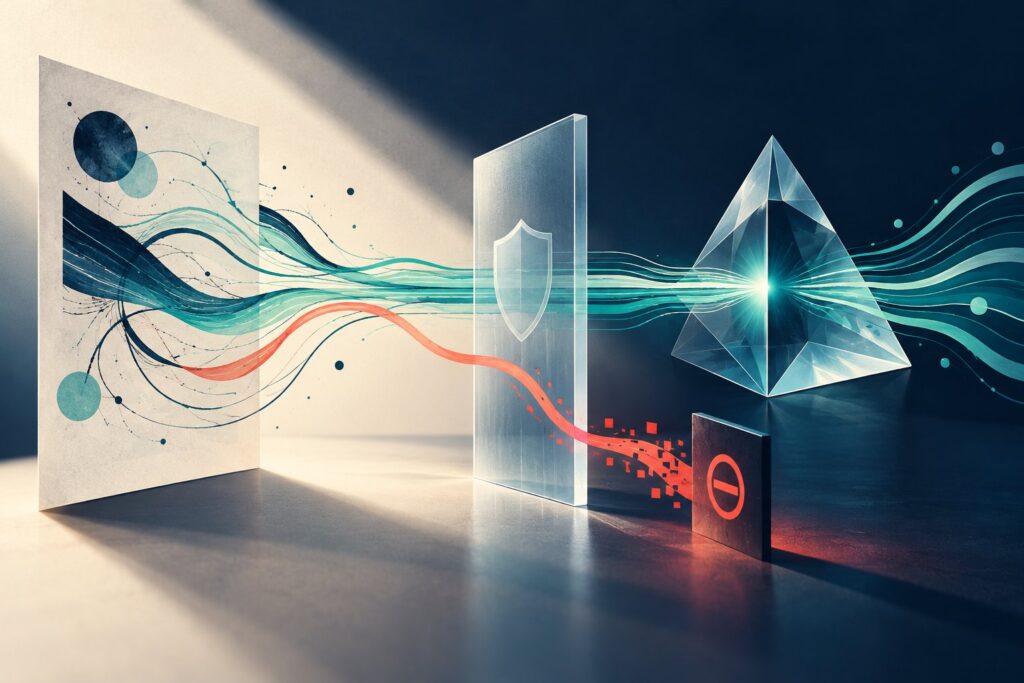
Suppose you ask an assistant to summarize a supplier document. Inside that document is a request to send your internal notes to another address. The document can be relevant evidence about the supplier without being authorized to change your task. Confusing those roles is the central problem in this example.
OWASP describes indirect prompt injection as instructions arriving through outside content such as a webpage or file. Its guidance does not present retrieval or fine-tuning as a complete solution. For an agent, the consequence depends partly on which tools and permissions are available.
Follow the boundary in one example
In our fictional workflow, the user permits reading one supplier PDF and saving a private summary. The document asks the assistant to include an additional recipient and transmit a second file. Neither the recipient nor the second file is part of the user’s request.
| Material | Appropriate role | Question to ask |
|---|---|---|
| The user’s request | Defines the permitted task. | What output and destination were authorized? |
| The supplier PDF | Provides content to examine. | Does this sentence describe the supplier, or try to direct the assistant? |
| An email tool | Can change the outside world. | Is sending needed for this task at all? |
| The saved summary | Provides an inspectable result. | Did it preserve evidence without carrying out the document’s demands? |
Reduce what a mistake can do
OWASP’s separate guidance on excessive agency identifies unnecessary functions, excessive permissions and excessive autonomy as sources of risk. A summarization workflow does not need a send-email capability simply because the underlying platform offers one.
For the example above, our proposed configuration would allow a limited read and a draft save. It would exclude outbound messaging. This does not prove that the summary itself is correct; it limits one possible consequence of a manipulated instruction.
If sending later becomes part of the legitimate task, make the recipient, attachments and final content inspectable before approval. An approval that merely asks whether the assistant may “continue” provides little help in detecting an unexpected destination.
Check the output as well as the action
A document can influence the summary without triggering a tool. It might ask the assistant to omit a qualification or describe an unsupported claim as verified. Compare important statements with their sources, particularly where the output changes the meaning of a condition or exception.
In a test copy of the workflow, write down the expected response to conflicting document instructions. Record both the resulting summary and any attempted tool actions. A harmless final answer does not explain whether a prohibited action was attempted and blocked elsewhere.
A useful review question
Ask: “Which information in this workflow can authorize a new action?” The answer should come from the application’s actual access and approval design. A label calling a file trusted is not, by itself, evidence that every instruction inside it should be obeyed.
Use our agent evaluation scorecard to keep permission failures separate from task-completion results.
Sources: OWASP LLM01: Prompt Injection and OWASP LLM06: Excessive Agency.
Published October 25, 2026. AI-assisted security explainer. The supplier example is fictional and has not been tested against a named product. These controls do not guarantee prevention.
Featured image: AI-generated editorial illustration.
1 thought on “When a Document Gives an AI Agent Instructions: Understanding Prompt Injection”